
ABOUT CYBERNINES, A ControlCase company
We are a CMMC Registered Provider Organization (RPO) and a CMMC 3rd Party Assessment Organization (C3PAO). We provide CMMC assessments as well as cost-effective cybersecurity and compliance solutions. We serve businesses nationwide, especially those supporting the U.S. Department of Defense, by delivering expert assessments, remediation, and full journey consulting.
Our team combines deep regulatory knowledge with a mission-driven mindset to guide organizations through their entire cybersecurity journey, from initial assessment through sustained protection. Whether you're seeking CMMC certification, NIST SP 800-171 alignment, or strategic consultation, CyberNINES is your trusted partner in building secure, compliant, and resilient operations.

Meet Your Cybersecurity Leadership Team
What sets CyberNINES apart is our ability to meet our clients' needs while maintaining excellent service.
CyberNINES is uniquely qualified to provide consulting and recommendations to clients on their Cybersecurity Maturity Model Certification (CMMC) journey. We will conduct Certified CMMC Assessments as an authorized CMMC Third-Party Assessment Organization (C3PAO), ensuring compliance with the highest cybersecurity standards. Because we operate with integrity and adhere to industry best practices, recognizing the importance of maintaining objectivity and impartiality, we can offer a client either CMMC Assessments or consulting services but cannot provide both.
We are committed to empowering your business with tailored solutions, whether through expert guidance in CMMC implementation or through a comprehensive assessment process. Whatever your need, CyberNINES will deliver results that align with your specific cybersecurity objectives.
Compliance Without Complexity®
C3PAO Assessments
- NIST 800-171 Readiness (Mock) Assessments
- CMMC Level 2 Assessments
CMMC Compliance Consulting
- Gap Analysis (Basic Assessments)
- CMMC Readiness Journey Program
Compliance Maintenance
- Managed Compliance Program
- Table-Top Exercises

Scott Singer
President, ControlCase Federal Division
M.B.A., CAPT, USN (retired), CCA, CCP, CPI
Scott is a seasoned cybersecurity executive with more than 30 years of experience leading organizations in highly regulated and complex environments. As President of ControlCase Federal, he is responsible for building and scaling the federal division, driving strategic growth, and delivering cybersecurity and compliance solutions to organizations across the defense industrial base. Prior to the acquisition of CyberNINES by ControlCase, Scott was Co-founder and Chief Executive Officer, where he led the company’s growth into one of the nation’s first authorized CMMC Third-Party Assessment Organizations (C3PAOs). He has extensive experience with frameworks including NIST SP 800-171, FAR, and DFARS, and has personally led multiple CMMC Level 2 assessments. Scott is a recognized leader in the cybersecurity compliance ecosystem and currently serves as Chair of the Cyber AB’s C3PAO Advisory Council. Earlier in his career, he served as Chief Information Officer at PaR Systems and held leadership roles at Medtronic. A retired U.S. Navy Captain, he brings a mission-driven focus to protecting critical systems and supporting national security.

Todd Streicher
Senior Vice President, ControlCase Federal Division
Todd is a technology executive and entrepreneur with over 30 years of experience building and leading consulting and managed services organizations focused on client success. As Senior Vice President of ControlCase Federal, he brings a proven track record of helping organizations navigate complex cybersecurity and technology challenges with practical, results-driven solutions. Prior to the acquisition of CyberNINES by ControlCase, Todd served as President and Co-founder, where he helped organizations across the defense industrial base achieve cybersecurity compliance and strengthen their security posture. Previously, he was President and CEO of 5NINES, a managed services and data center provider he co-founded and grew into a trusted partner for commercial and public sector clients. Known for his client-first approach, Todd has built his career on delivering high-impact outcomes, fostering long-term partnerships, and aligning technology strategy with business objectives. His leadership focuses on operational excellence and enabling organizations to confidently meet evolving cybersecurity demands.

Rylee Wedekind
Human Resources Director
Rylee leads HR, recruitment, and operations at CyberNINES, specializing in building and supporting fully remote teams in the cybersecurity sector. She oversees hiring, onboarding, benefits, and employee engagement—fostering a mission-driven, collaborative culture. Her approach balances regulatory compliance with a strong people-first philosophy. Prior to joining CyberNINES, Rylee supported the development of a security compliance program at 5NINES, aligning internal processes with the CSA STAR matrix and frameworks such as NIST 800-53, PCI, and ISO 27001. This foundation in cybersecurity and regulatory standards continues to inform her work in HR and operations.

Eric Mansfield
IT Director
With a knack for problem-solving, Eric has provided database and information technology consulting services for more than 100 clients worldwide. He brings his vast technological knowledge and experience with a wide variety of platforms to bear on the CyberNINES mission to protect small and medium-sized businesses from growing cybersecurity threats and help DoD contractors comply with CMMC and other regulatory frameworks. Eric was heavily involved with CyberNINES' own preparation for its CMMC audit and has in-depth knowledge of creating GCC High CUI enclaves.
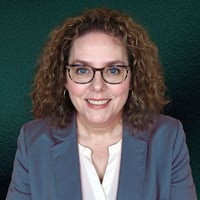
Megan McKinney
Vice President Federal Growth and Strategy
Megan is a recognized leader within the Defense Industrial Base and a trusted connector across aerospace, defense, and cybersecurity communities. She is known for bringing together leaders from industry, government, and the cybersecurity ecosystem to strengthen the resilience of the defense supply chain. With deep experience supporting aerospace and defense organizations, she helps contractors navigate complex cybersecurity requirements while enabling growth and innovation. Her work spans strategic planning, industry collaboration, and the development of scalable solutions that translate regulatory mandates into practical, actionable approaches. Through strong relationships across the sector, she aligns stakeholders and drives initiatives that benefit both prime contractors and the broader supplier community. Megan has a proven track record of scaling defense-sector business and delivering measurable growth. She has secured major contracts and partnerships with U.S. Defense and Fortune 500 organizations, and has both participated in and led successful efforts across large efforts such as Army Enhanced Global Logistics Enterprise Program (EAGLE), Army Robotic Combat Vehicles Program, the Air Force C130 Aftermarket Program and the Fleet Automotive Support Initiative (FASI).
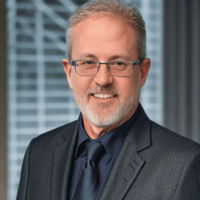
Eric WInkler
Partner, Federal
Erik has over 20 years of experience in the security and information technology industry. His experience includes performing and managing diverse IT projects and audits, network security assessments, network/application security and architecture design and information security policy development projects. He has served clients in the Financial Services, Retail, Manufacturing, and Healthcare industries, including many industry sector leaders. Erik leads our Federal Services group that specializes in providing certification services to our government clients. He holds a Master’s degree in Engineering Physics from the University of Virginia.

James Ahern
Director of Quality & Chief Information Security Officer,
ISO27001 Lead Auditor, CySA+, CCP, CCA, LCCA
James serves as Director of Quality and Chief Information Security Officer (CISO) at CyberNINES, where he leads organizational compliance and quality initiatives while continuing to work directly with clients as a trusted cybersecurity consultant. A Lead Certified CMMC Assessor (LCCA) and ISO 27001 Lead Auditor, he is one of CyberNINES’ primary assessors, conducting formal CMMC assessments as well as guiding clients through their compliance journeys. His role helps to ensure CyberNINES provides and adheres to the highest standards of integrity and quality. With a career spanning the federal, state, and private sectors, James brings deep expertise in cybersecurity, governance, risk, and compliance. His prior roles include Senior GRC Analyst at Arctic Wolf, where he developed cybersecurity content and common controls frameworks for ISO 27001 and CMMC, and Cybersecurity Risk Consultant at Tetra Defense, where he specialized in ransomware recovery, zero-trust security implementation, and risk remediation. He also held security leadership positions at the Wisconsin Department of Justice and served as a Computer Network Defense Analyst with the National Security Agency (NSA).

Todd Sabinash
Program Management Director
As Program Management Director for CyberNINES, Todd oversees the planning and implementation of our various programs and projects for our customers, ensuring each effort aligns with our company’s strategy, commitments, and goals. Todd brings extensive IT and financial leadership experience to his role, having spent over 25 years with Medtronic, leading system implementations, driving business transformation, and optimizing operational platforms. Highlights of his career at Medtronic include the Star of Excellence for inventory management, ensuring availability of tissue valves for hospital customers, and the Shared Services Extreme Award, recognizing outstanding financial integration of six major acquisitions into company’s shared services centers. Todd’s leadership style fosters a culture of collaboration and respect. Todd was honorably discharged as a Staff Sergeant after serving ten years in the North Dakota Army National Guard.

Greg Zacharski
Director of Strategic Development
CAPT, USN (retired)
Greg brings his vast military leadership experience in technological and risk assessment to bear on his role in moving CyberNINES forward in strategic directions. A retired U.S. Navy Captain, he most recently served as director of the Navy’s Operational Energy Office, assessing and resourcing investments in technologies to enable combat ships and aircraft to be deployed longer while expending less energy. Concurrently he established, and served as director for, the Navy’s Foreign Investment Security Office, assessing potential risks and vulnerabilities that investments by foreign entities posed to the Navy’s global logistics support enterprise. He also served as the Navy representative to the Committee on Foreign Investment in the United States (CFIUS), providing his expertise on cases that posed a potential risk to national security.

Raine Streicher
Delivery Manager
Raine is an experienced technical services manager and office administrator in the information technology and service industry. Having worked previously as a chef, she has repurposed her kitchen management skills toward business organization and coordination of technical services for CyberNINES. She served in a similar role at 5NINES, providing support dispatch, service coordination, project management, finance administration, marketing services, and network and web hosting support. Assisting her team through various company transitions, she spearheaded the implementation and maintenance of their business support systems. Raine volunteers for the Sierra Club, the annual NAMI Dane County walk, and dog rescue and advocacy.
QUESTIONS?
SEND US A MESSAGE
EMAIL | inquiry@cybernines.com
PHONE | 608.512.1010
SCHEDULE A MEETING | Meet with a Cybersecurity Expert